1
Aruba 6000 and Aruba 800 series Mobility Controller Security Target
Version
1.8
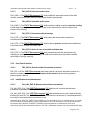
FTP_ITC_EXP.1.3a The TSF shall initiate communication via the trusted channel for [all
authentication functions, remote logging, time].
Application Note: The trusted channel is based on the IPSec/IKE protocol with pre-shared keys.
5.1.8.2
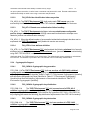
FTP_TRP.1a Trusted path (remote administrators)
FTP_TRP.1.1a
The TSF shall provide a communication path between itself and remote
administrators that is logically distinct from other communication paths and provides assured
identification of its end points and protection of the communicated data from modification, replay or
disclosure.
FTP_TRP.1.2a
The TSF shall permit remote administrator client devices to initiate
communication via the trusted path.
FTP_TRP.1.3a
The TSF shall require the use of the trusted path for remote administrator
user authentication.
Application Note: The TOE provides a TLS based trusted path from the remote administrator to the TOE for
authentication as a wired user against the external RADIUS authentication server using a username and
password.
5.1.8.3
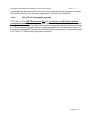
FTP_TRP.1b Trusted path (wireless users)
FTP_TRP.1.1a
The TSF shall provide a communication path between itself and wireless
users that is logically distinct from other communication paths and provides assured identification of
its end points and protection of the communicated data from modification, replay or disclosure.
FTP_TRP.1.2a
the trusted path.
The TSF shall permit wireless client devices to initiate communication via
FTP_TRP.1.3a
authentication.
The TSF shall require the use of the trusted path for wireless user
Application Note: This SFR applies to the authentication of wireless users using an open system connection.
In this case, an IPSec/IKE VPN using a pre-shared key is set up between the wireless user and the TOE prior
to user authentication to the external RADIUS server using a username and password. The VPN protects the
user authentication.
Application Note: As specified in the requirement FTP_TRP.1c for the IT Environment, the authentication
server establishes a trusted path between the authentication server and the wireless client which passes
through the TOE. This trusted path is used for wireless user authentication during EAP-TLS, EAP-TTLS or
PEAP authentication phase.
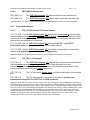
5.2 Security Requirements for the IT Environment.
This ST includes functional requirements for the IT Environment. The IT environment includes the
authentication server, the NTP time server and the audit server.
In support of the audit server, the environment shall provide the capability to store and protect audit
information. The environment shall also provide the capability to selectively view audit data.
Page 39 of 101