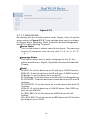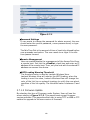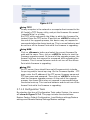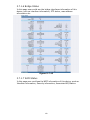
1
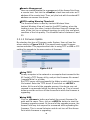
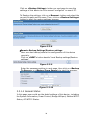
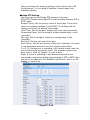
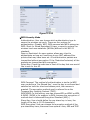
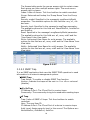
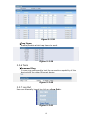
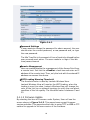
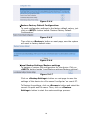
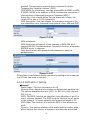
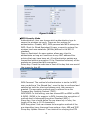
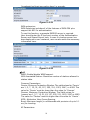
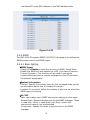
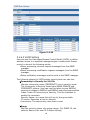
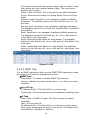
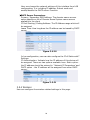
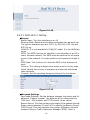
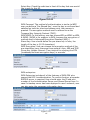
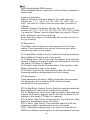
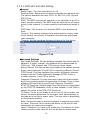
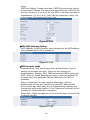
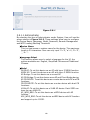
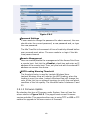
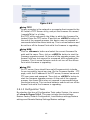
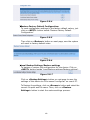
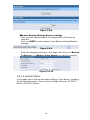
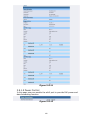
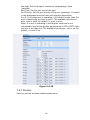
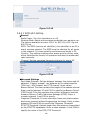
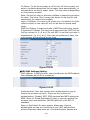
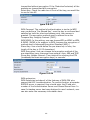
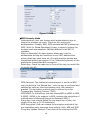
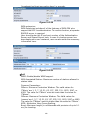
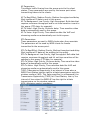
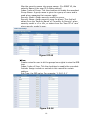
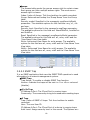
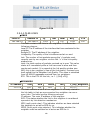
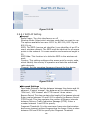
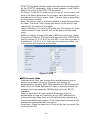
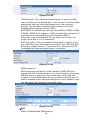
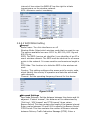
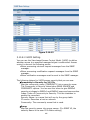
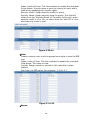
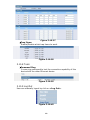
WPA-Personal: The method of authentication is similar to WEP, user can define a ‘Pre-Shared Key’, once the key is confirmed and satisfied on both the client and access point, then access is granted. The encryption method used is referred to as the Temporal Key Integrity Protocol (TKIP). WPA MODE: In this setting, user can choose WPA or WPA2 or WPA & WPA2. (WPA2 is far superior to WPA, because the encryption of method used is Advanced Encryption Standard (AES)). Share Key: User should define the pre-share key in here; the length of the key is (8-23 characters). WPA Encryption: User can choose the encryption method of the pre-shared key here; there are three options: Auto, AES and TKIP. Group Key Update Interval: Time interval for rekeying the GTK (broadcast/multicast encryption keys) in seconds. Figure 3-7-23 WPA-enterprise: WPA-Enterprise includes all of the features of WPA-PSK plus support the 802.1x authentication. To use this function, a separate RADIUS server is required. User should enter the IP and port number of the Authentication Server and Shared Secret here. In case if a backup server has been deployed in user’s network, user can also enter the necessary information here. Figure 3-7-24 QoS WMM: Enable/disable WMM support. MAX Associated Station: Maximum number of stations allowed in station table. Common Parameters: 139