1
Chapter 4 - Managed Switch Software Setup
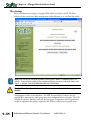
IKE Certificates
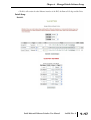
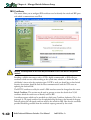
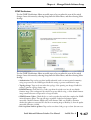
This screen allows you to configure IKE certificates used to identify the switch and IKE peers
with which it communicates over IPv6.
Warning: Misconfiguration on this screen may block network access to the Switch’s configuration
interface.
Providing a reliable time source, such as NTP, is highly recommended, as IKE will reject
certificates which are not valid according to the system time, whether it is before the 'not
valid before' time or after the expiration time. If NTP is used, pre-shared keys or hard-wired
Security Associations should be used for IPsec communications with the NTP server or
updating the clock will fail.
The HTTPS certificate used by the switch's Web interface cannot be changed on this screen.
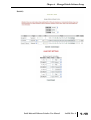
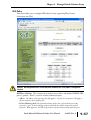
Switch Certificate: This section may be used to generate or view the details of an X.509
certificate which the switch uses to identify itself via IKE.
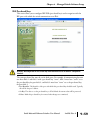
A certificate request which can be provided to a third-party Certificate Authority (CA) is also
generated. A CA-signed certificate can be uploaded using the form at the bottom of the page
and will replace the self-signed certificate used by the switch for IKE. Note that the certificate
provided should be generated from the certificate request generated by the switch.
4–60
Stride Industrial Ethernet Switches User Manual
2nd Ed. Rev. A