1
1.5.3
Person Determining CPS Suitability for the Policy
The term CPS is defined in the [RFC 3647] as: "A statement of the practices, which a Certification Authority
employs in issuing Certificates.”. It is a comprehensive description of such details as the precise
implementation of service offerings and detailed procedures of Certificate life-cycle management. It shall be
more detailed than the corresponding Certificate Policy defined above and reference all internal document of
the OA (classified documentation).
A CPS may be approved as sufficient for fulfilling the obligations under this CP when such a CPS has been
reviewed by an auditor or compliance analyst competent in the operations of a PKI, and when said person
determines that the CPS is in fact in compliance with all aspects of this CP. The auditor or compliance
analyst shall be designated by PMA. Additionally, the auditor or compliance analyst may not be the author of
the subject CPS and maybe internal employee of OpenTrust.
The PMA approves the CPS. The PKI will be audited periodically to verify compliance as per PMA guidelines
and standards approved by the PMA. The Audit ensures that the CPS is implemented correctly and is
compliant with the CP. Further, the PMA reserves the right to audit the PKI as set in section 8 of this CP.
1.5.4
CPS Approval Procedures
Amendments shall either be in the form of a new CPS (with a sum up of the modifications) or an update
notice that contains the modifications and the references in the previous CPS. The creation or modification of
the existing CPS is at the discretion of the PMA. A new CPS automatically replaces the previous one and
becomes operational as soon as the PMA has approved it. Any new CPS or update to the existing CPS must
be verified compliant with this CP before approval.
1.6
1.6.1
Definitions and Acronyms
Definitions
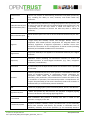
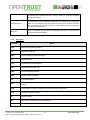
Term Accreditation Definition Formal declaration by a Designated Approving Authority that an Information System is approved to operate in a particular security mode using a prescribed set of safeguards at an acceptable level of risk. Activation Data Secret data (e.g.: password, PIN code, certificate or OTP) that is used to perform cryptographic operations using a Private Key. Audit An independent review and examination of documentation, records and activities to access the adequacy of system controls, to ensure compliance with established policies and operational procedures, and to recommend necessary changes in controls, policies or procedures. Authentication The process whereby one party has presented an identity and claims to be that identity and the second party confirms that this assertion of identity is true. Authentication data Particular technical activation data (like for example OTP or authentication certificate) used by Subscriber to be authenticated by Protect and Sign (Personal signature) service in order to sign a document according a © OpenTrust. All rights reserved.
Ref : OpenTrust_DMS_RCA Program_OpenTrust_CP v 1.2
- 21 -
www.opentrust.com