1
Chapter 13
Technical introduction to Hybrid
enforcement
Introduction
Before version 3.6 of PacketFence, it was not possible to have RADIUS enabled for inline enforcement
mode. Now with the new hybrid mode, all the devices that supports 802.1x or mac-auth can work with
this mode. Let’s see how it works.
Device configuration
You need to configure inline enforcement mode in PacketFence and configure your switch(es) / access
point(s) to use the VLAN assignement techniques (802.1x, mac-auth). You also need to take care of a
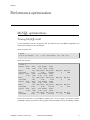
specific parameter in the switch configuration window, "Trigger to enable inline mode". This parameter
is working like a trigger and you have the possibility to define different sort of trigger:
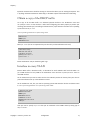
ALWAYS , PORT ,
MAC , SSID
where ALWAYS means that the device is always in inline mode, PORT specify the
ifIndex of the port which will use inline enforcement, MAC a mac address that
will be put in inline enforcement technique rather than VLAN enforcement and
SSID an ssid name. An example:
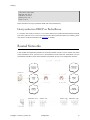
SSID::GuestAccess,MAC::00:11:22:33:44:55
This will trigger all the nodes that connects to the "GuestAccess" SSID to use inline enforcement mode
(PacketFence will return a void VLAN or the inlineVlan if defined in switch configuration) and the mac
address 00:11:22:33:44:55 client if it connects on another SSID.
Copyright © 2008-2013 Inverse inc.
Technical introduction
to Hybrid enforcement
84