1
VIRUS BULLETIN www.virusbtn.com
NEWS
NO MAIL FOR ALISONS, ALBERTS,
ALGERNONS...
McAfee customers whose email address begins with the
letter ‘A’ may have found their inboxes unexpectedly
quiet earlier this month when a flawed update script in
the MX Logic managed email filtering service (acquired
by McAfee in 2009) prevented them from receiving mail.
According to McAfee, temporary account verification issues
were experienced by users with non-alphanumeric email
addresses and aliases up to the letter ‘A’. The issue was
identified and fixed within 12 hours.
This is not the first time an innocent letter has caused
problems and red faces for a security firm – in 2003, Trend
Micro quarantined the letter ‘P’, when a bug in an update for
email security product eManager quarantined all incoming
mail containing the letter ‘P’ (see VB, June 2003, p.3).
OLD BREACH REARS ITS HEAD
The potential long-lasting effects of a security breach were
highlighted earlier this month when a small Illinois-based
bank revealed that customers’ payment card information had
been compromised at card processor Heartland Payment
Systems – which suffered a breach back in 2008.
It is thought that, more than two years after the breach,
crooks are still working their way through the stolen card
details. While many of the cards will no longer be active
after such a long period of time (either because they have
expired or because they have been cancelled), the flip side
is that if a credit card has gone for two years without any
signs of fraudulent activity, banks and retailers are likely to
assume that it hasn’t been stolen – thus making it easier for
the criminals to defraud.
The news comes just days after email marketing firm
Epsilon admitted that hackers had obtained access to its
customer data. The Dallas-based company claims that the
data breach affected only around 2% of its clients and that
the information obtained was limited to email addresses
and/or customer names only. However, a growing list of
companies is known to have had their customer lists stolen.
Among the victims are Hilton Honors, Walgreens, Disney
Destinations, Marks and Spencer, Capital One, TiVo,
JPMorgan Chase and Citibank.
Even if the hackers did only obtain names and email
addresses, these companies’ customers will now be at
increased risk of phishing – and with the crooks able to
personalize their emails, the phishes will be harder to spot
than generic ones. Most of the affected companies have
warned their customers to be on the alert for phishing
attempts.
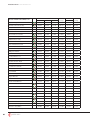
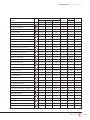
Prevalence Table – February 2011 [1]
Malware
Autorun
VB
Conficker/Downadup
Agent
FakeAlert/Renos
Exploit-misc
Adware-misc
Downloader-misc
Delf
OnlineGames
Injector
Sality
Heuristic/generic
StartPage
Kryptik
Small
Heuristic/generic
AutoIt
Hupigon
Zbot
Dropper-misc
Heuristic/generic
Crack/Keygen
Iframe
Alureon
PDF
Bifrose/Pakes
Virtumonde/Vundo
Tanatos
Virut
PCClient
Hoax
Type
Worm
Worm
Worm
Trojan
Rogue AV
Exploit
Adware
Trojan
Trojan
Trojan
Trojan
Virus
Virus/worm
Trojan
Trojan
Trojan
Misc
Trojan
Trojan
Trojan
Trojan
Trojan
PU
Exploit
Trojan
Exploit
Trojan
Trojan
Worm
Virus
Trojan
PU
Others [2]
Total
[1]
%
9.13%
7.43%
5.75%
5.00%
4.53%
3.86%
3.68%
3.49%
2.89%
2.81%
2.66%
2.35%
2.17%
2.09%
2.06%
1.77%
1.54%
1.50%
1.49%
1.46%
1.40%
1.40%
1.33%
1.28%
1.27%
1.20%
1.18%
1.12%
1.10%
1.07%
0.89%
0.81%
18.28%
100.00%
Figures compiled from desktop-level detections.
[2]
Readers are reminded that a complete listing is posted at
http://www.virusbtn.com/Prevalence/.
APRIL 2011
3