1
Introduction
•
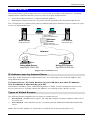
Special Internet Applications. Internet applications such as Internet Videoconferenc-
•
DMZ. One (1) PC on your local LAN can be configured to allow unrestricted 2-way
•
URL Filter. Use the URL Filter to block access to undesirable Web sites by LAN users,
Wireless LAN users, or the Dial-in user.
•
Internet Access Log. See which Internet connections have been made.
ing, Telephony, Games Servers, and other special-purpose Servers are supported.
communication with Servers or individual users on the Internet.
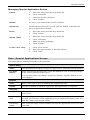
RAS (Remote Access Services)
•
RAS Dial-in. Remote PC users can use their standard Dial-up software to connect to the
Wireless Router and access LAN resources.
•
Dial-back Support. For additional security, the Dial-back feature can be used to hang up
and re-dial the remote user. Both fixed and roaming options are supported.
Configuration & Management
•
Easy Setup. Use your WEB browser from anywhere on the LAN for configuration.
•
Remote Management. The Wireless Router can be managed from any PC on your
LAN. And, if the Internet connection exists, it can also (optionally) be configured via the
Internet.
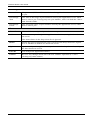
Security Features
•
Configuration Data. Optional password protection is provided to prevent unauthorized
•
Access Control Features. The LAN Administrator can limit Internet access by individ-
•
Wireless LAN Security. WEP (Wired Equivalent Privacy) is supported, as well as
•
Firewall Protection. All incoming data packets are monitored and all incoming server
users from modifying the configuration.
ual workstations. And the Access Control log allows the Administrator to see attempted
accesses which have been blocked.
Wireless access control via station address.
requests are filtered, thus protecting your network from malicious attacks from external
sources. (This protection is lost if NAT is disabled.)
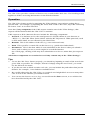
NAT Firewall Protection
The firewall protection provided by the Wireless Router is an intrinsic side effect of
NAT (Network Address Translation). All users on the LAN share a single external
IP address. From the external viewpoint, there is no network, only a single device.
For internal users, the Wireless Router acts as a “transparent proxy server”,
translating the multiple internal IP addresses into a single external IP address.
For external requests, any attempt to connect to local resources is blocked. The
Wireless Router will not “reverse translate” from a external IP address to a local IP
address.
This type of “natural” firewall provides an impregnable barrier against malicious
attacks.
3