1
Programming with security in mind
1.36.3
181
Do not assume correct input
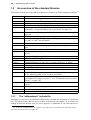
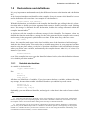
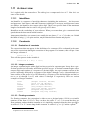
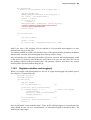
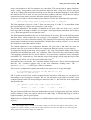
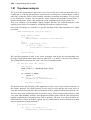
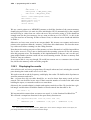
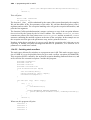
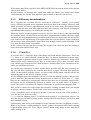
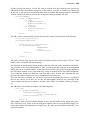
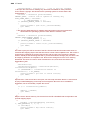
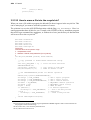
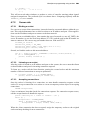
Do you remember the Blaster worm?
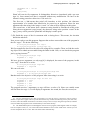
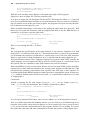
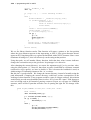
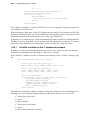
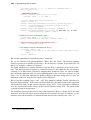
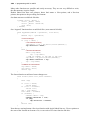
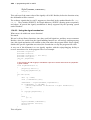
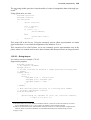
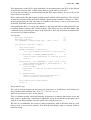
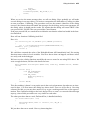
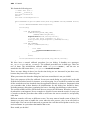
Here is the code that allowed the Blaster worm to exist:83
HRESULT GetMachineName(WCHAR *pwszPath) {
WCHAR wszMachineName[N + 1])
LPWSTR pwszServerName = wszMachineName;
while (*pwszPath != L'\\' )
*pwszServerName++ = *pwszPath++;
...
}
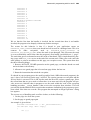
The error here is the assumption that the path is a reasonable path that will not overrun the destination buffer. Machine names are normally at most 10-15 chars long. If you are not expecting unreasonable input, you can just use the above code. And that code was running for quite a
long time before this time bomb exploded and a clever hacker found out that he/she could gain
control of the machine with this sloppy programming snippet.
1.36.4
Watch out for trojans
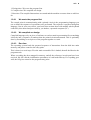
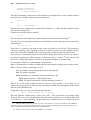
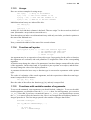
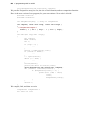
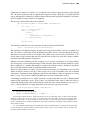
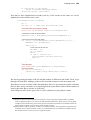
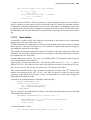
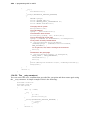
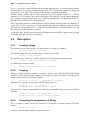
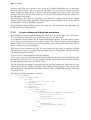
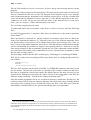
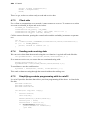
The windows API CreateProcess, can be given the name of the program to execute in two
ways: as its first argument, or as a whole command line in its second parameter, leaving the
first empty as NULL. Suppose this:
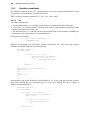
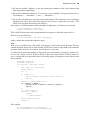
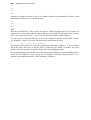
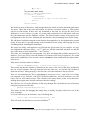
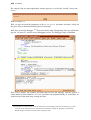
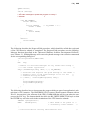
CreateProcess(NULL, "C:\\Program Files\\myprogram.exe", ...)
Suppose now, that somebody has left a “c:\program.exe” executable in the right place. What
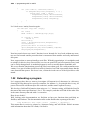
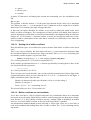
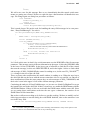
will happen? CreateProcess will start executing “c:\program” instead of the indicated program. A simple way to avoid this is to enclose the name of the program in quotes.
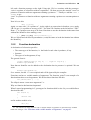
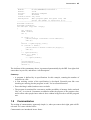
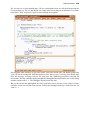
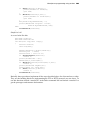
CreateProcess(NULL, "\"C:\\Program Files\\myprogram.exe\" -K -F",
...)
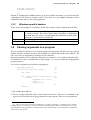
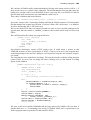
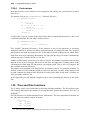
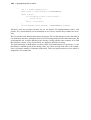
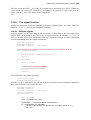
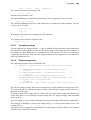
Notice that the related API WinExec will scan its input for the first space, making it worst than
CreateProcess. In the above example, the code:
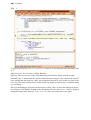
WinExec(“C:\\program files\\myprogram.exe”);
will always try to execute c:\program if it exists.
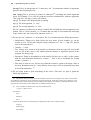
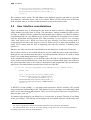
83. Microsoft Security Bulletin MS03-026: Buffer Overrun In RPC Interface Could Allow Code Execution (823980). Originally posted: July 16, 2003. Revised: September 10, 2003. Cited by Michael Horward in his excellent series about security in msdn. The URL for one of its articles is: http://
msdn.microsoft.com/library/default.asp?url=/library/en-us/dncode/html/secure09112003.asp