1
V2616 Linux User's Manual
Managing Communications
Ethernet Bridging for Private Networks on Different Subnets
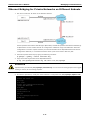
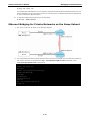
1. Set up four machines, as shown in the following diagram.
Host A represents the machine that belongs to OpenVPN A, and Host B represents the machine that belongs
to OpenVPN B. The two remote subnets are configured for a different range of IP addresses. When this
configuration is moved to a public network, the external interfaces of the OpenVPN machines should be
configured for static IPs, or connected to another device (such as a firewall or DSL box) first.
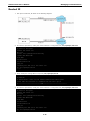
2. Generate a preset shared key by typing the following command:
# openvpn --genkey --secret secrouter.key
3. Copy the file that is generated to the OpenVPN machine:
# scp /etc/openvpn/secrouter.key 192.168.8.174:/etc/openvpn
ATTENTION
A preshared key is located at /etc/openvpn/secrouter.key. You can use it for testing purposes. We suggest
creating a new key for non-testing purposes.
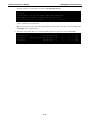
4. On machine OpenVPN A, modify the remote address in configuration file /etc/openvpn/tap0-br.conf.
# point to the peer
remote 192.168.8.174
dev tap0
port 1194
secret /etc/openvpn/secrouter.key
cipher DES-EDE3-CBC
auth MD5
tun-mtu 1500
tun-mtu-extra 64
ping 40
up /etc/openvpn/tap0-br.sh
#comp-lzo
3-21