1
Brocade Encryption Switch/Blade
Remote server Subnet
topology
Configuration overview
In this type of topology, the RKM Servers and the Virtual IP address
(VIP) that the Encryption devices will establish connections to are on
two different logical Layer 3 subnets. However, the primary
differences between this topology and the Routed Topology is that
the RKM servers do not have the ADX set as their default gateway
and typically reside on a subnet that is reachable via Layer 3 IP
routing. In order for this topology to work, Network Address
Translation (NAT) is a requirement as traffic initiated from the
Encryption Device will automatically flow back through the ADX.
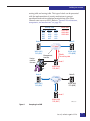
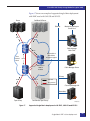
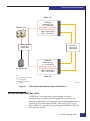
Figure 37 on page 262 is a basic illustration of a Remote Server Subnet
topology configuration where the ADX1000 is on a completely
different Layer subnet than the RKM Servers. The Brocade
Encryption Device and RKM clients can be on completely different
subnets as long as the Routing on the network is in place to reach the
VIP. The two ADX1000 units are also attached to each other to
provide a failover path.
SRDF encryption case study
261