1
Processor Reference
code of the page. If a user finds the hidden link code in the HTML, and attempts to get a directory file
listing from the directory the link points to, this incident will be triggered.
Behavior: A common technique for hackers when scoping the attack surface of a website is to spider the
site and collect the locations of all of its pages. This is generally done using a simple script that looks for
URL's in the returned HTML of the home page, then requests those pages and checks for URL's in their
source, and so forth. Legitimate search engine spiders will do this as well. But the difference between
a legitimate spider and a malicious user, is how aggressively they will use the newly discovered URL to
derive other URLs. This incident triggers when the user goes beyond just checking the linked URL, but
instead also attempts to get a file listing from the directory the URL points to. A legitimate spider would
not do this, because it is considered fairly invasive. This activity is generally looking for a "Directory
Indexing [http://projects.webappsec.org/Directory-Indexing]"weakness on the server, in an effort to locate
unlinked and possibly sensitive resources.
Incident Name: Link Directory Spidering
Complexity: Medium
Default Response: 1x = Slow Connection 2-6 seconds and 5 Day Block in 6 minutes.
Cause: MWS injects a hidden link into pages on the protected web application. This link is not exposed
visually to users of the website. In order to find the link, a user would need to manually inspect the source
code of the page. If a user finds the hidden link code in the HTML, and attempts to request some other
arbitrary file in the same fake directory as the link, this incident will be triggered.
Behavior: A common technique for hackers when scoping the attack surface of a website is to spider the
site and collect the locations of all of its pages. This is generally done using a simple script that looks
for URL's in the returned HTML of the home page, then requests those pages and checks for URL's in
their source, and so forth. Legitimate search engine spiders will do this as well. But the difference
between a legitimate spider and a malicious user, is how aggressively they will use the newly discovered
URL to derive other URLs. This incident triggers when the user goes beyond just checking the linked
URL, but instead also attempts to request one or more arbitrary files inside the same directory as the file
referenced by the hidden link. A legitimate spider would not do this, because it is considered fairly invasive.
This activity is generally looking for a "Directory Indexing [http://projects.webappsec.org/DirectoryIndexing]" weakness on the server, or a "Predictable Resource Location" [http://projects.webappsec.org/
Predictable-Resource-Location] vulnerability, in an effort to locate unlinked and possibly sensitive
resources.
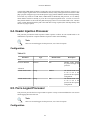
3.8. Query String Processor
Hackers tend to manipulate the values of query string parameters in order to get the application to behave
differently. The goal of this processor is to add fake query string parameters to some of the links and forms
in the page, and verify that they do not get modified when accessed by the user.
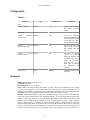
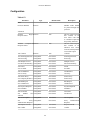
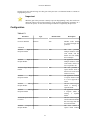
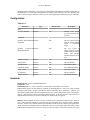
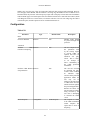
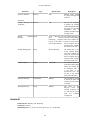
Configuration
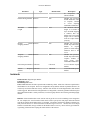
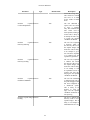
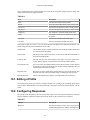
Table 6.8.
Parameter
Type
Default Value
Basic
38
Description