1
CAMBIUM NETWORKS
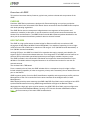
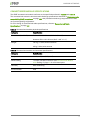
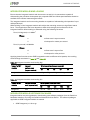
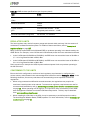
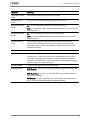
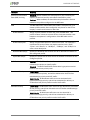
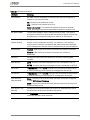
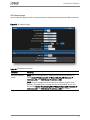
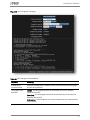
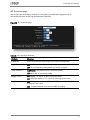
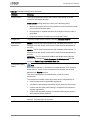
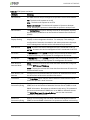
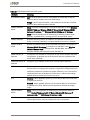
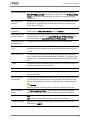
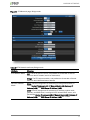
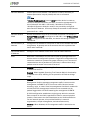
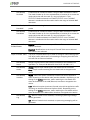
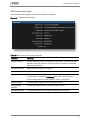
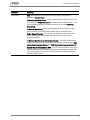
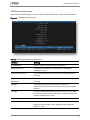
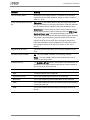
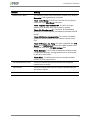
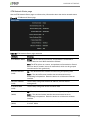
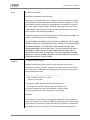
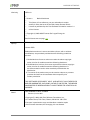
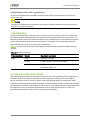
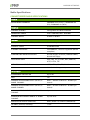
Table 58 STA Security attributes
Attribute
Meaning
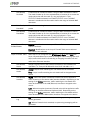
Authentication Preshared Key
Configure this key on the AP, then configure each of the network STAs
with this key to complete the authentication configuration. This key
must be between 8 to 128 symbols.
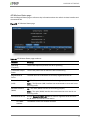
Layer 2 Firewall Entry
Enable/Disable
Enabled: Modifications to the Layer 2 Firewall Table are allowed and
rules are enforced
Disabled: Modifications to the Layer 2 Firewall Table are not allowed
and rules are not enforced
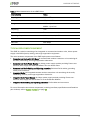
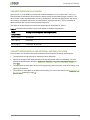
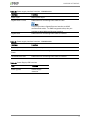
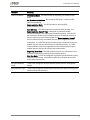
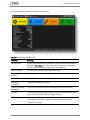
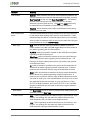
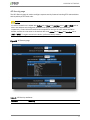
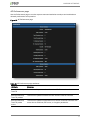
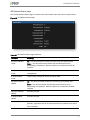
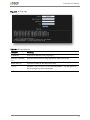
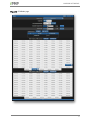
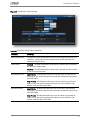
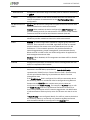
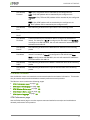
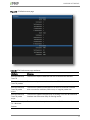
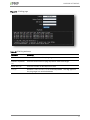
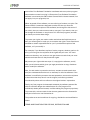
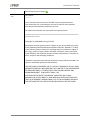
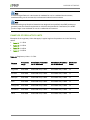
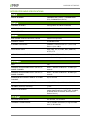
Layer 2 Firewall Table
The Layer 2 firewall table may be used to configure rules matching layer
2 (MAC layer) traffic which result in forwarding or dropping the traffic
over the radio link or Ethernet interface.
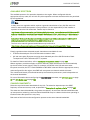
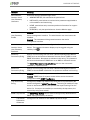
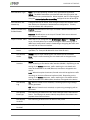
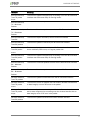
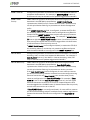
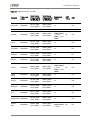
Rule Details,
Name
Assign a logical name to the firewall rule based on the intended rule
operation (i.e. “Deny all WLAN traffic from VLAN ID 100”)
Rule Details,
Action
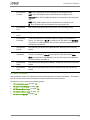
Accept: Layer 2 traffic matching the rule details will be forwarded
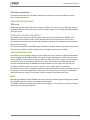
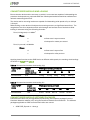
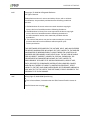
Rule Details,
Interface
WLAN: When this option is selected, firewall rules will be applied to
traffic incoming on the device radio interface (WLAN). Depending on the
setting of the Action parameter, traffic matching the rule details will
either be forwarded to the LAN (Ethernet) interface or dropped at the
device.
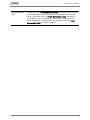
Deny: Layer 2 traffic matching the rule details will be dropped at the
device
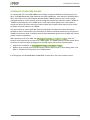
LAN: When this option is selected, firewall rules will be applied to traffic
incoming on the device Ethernet interface (LAN). Depending on the
setting of the Action parameter, traffic matching the rule details will be
either forwarded to the WAN (radio) interface or dropped at the device
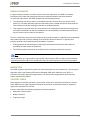
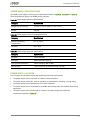
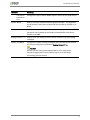
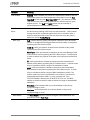
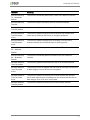
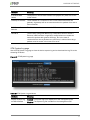
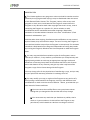
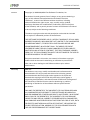
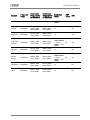
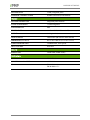
Rule Details,
Log
On: When a firewall rule is matched, a resulting system log message
will be generated
Off: When a firewall rule is matched, no system log messaging will be
generated
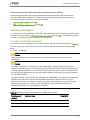
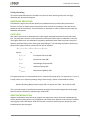
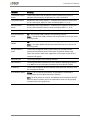
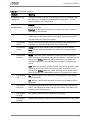
Rule Details,
EtherType
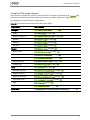
Rule matching is based on the two octet Ethertype field in the Ethernet
frame. The Ethertype is used to identify the protocol of the data in the
payload of the Ethernet frame.
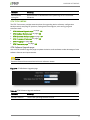
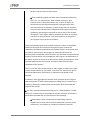
Rule Details,
VLAN ID
Rule matching is based on the VLAN ID of the packet
Rule Details,
Src MAC
Firewall rule matching is based on the source MAC address of the packet
143