1
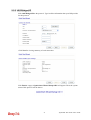
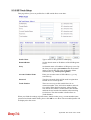
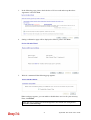
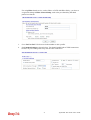
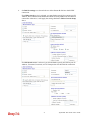
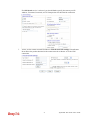
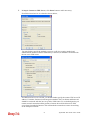
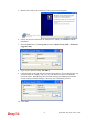
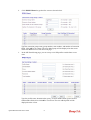
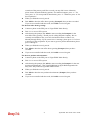
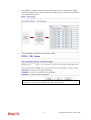
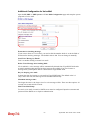
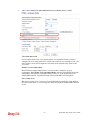
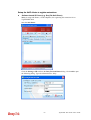
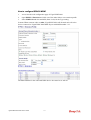
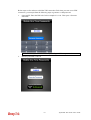
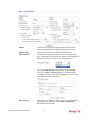
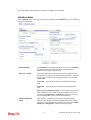
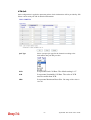
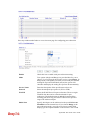
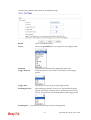
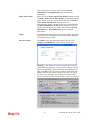
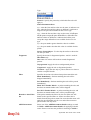
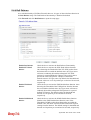
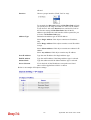
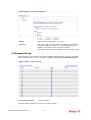
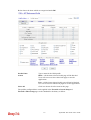
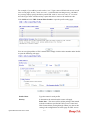
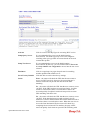
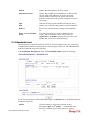
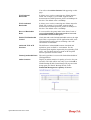
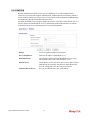
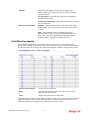
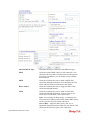
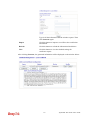
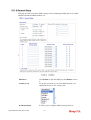
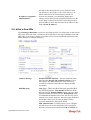
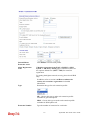
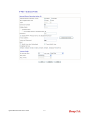
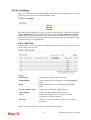
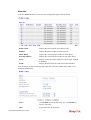
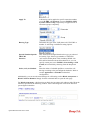
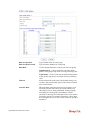
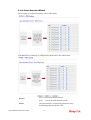
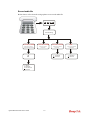
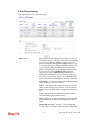
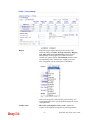
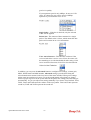
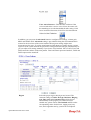
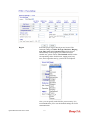
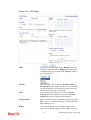
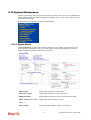
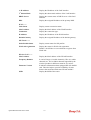
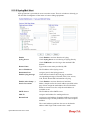
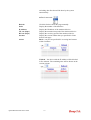
IPSec Security Method
Medium
Advanced
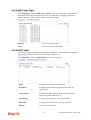
Pre-Shared Key - Input 1-63 characters as pre-shared
key.
Digital Signature (X.509) - Select one predefined
Profiles set in the VPN and Remote Access >>IPSec
Peer Identity.
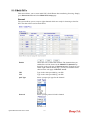
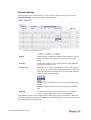
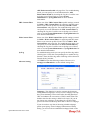
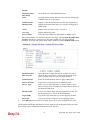
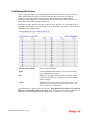
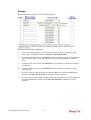
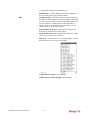
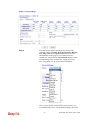
This group of fields is a must for IPSec Tunnels and L2TP
with IPSec Policy.
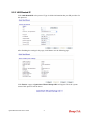
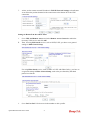
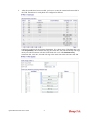
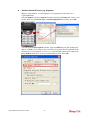
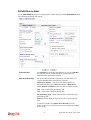
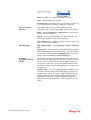
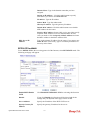
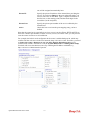
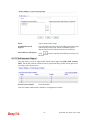
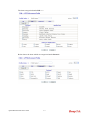
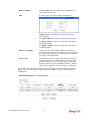
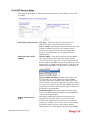
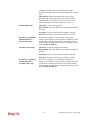
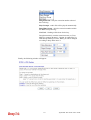
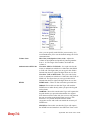
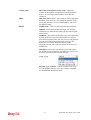
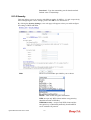
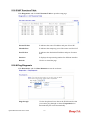
Medium (AH) means data will be authenticated, but not
be encrypted. By default, this option is active.
High (ESP-Encapsulating Security Payload)- means
payload (data) will be encrypted and authenticated. Select
from below:
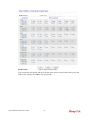
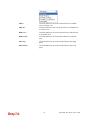
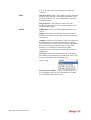
DES without Authentication -Use DES encryption
algorithm and not apply any authentication scheme.
DES with Authentication-Use DES encryption algorithm
and apply MD5 or SHA-1 authentication algorithm.
3DES without Authentication-Use triple DES encryption
algorithm and not apply any authentication scheme.
3DES with Authentication-Use triple DES encryption
algorithm and apply MD5 or SHA-1 authentication
algorithm.
AES without Authentication-Use AES encryption
algorithm and not apply any authentication scheme.
AES with Authentication-Use AES encryption algorithm
and apply MD5 or SHA-1 authentication algorithm.
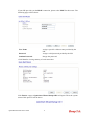
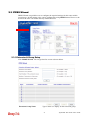
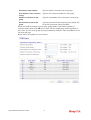
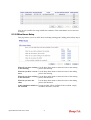
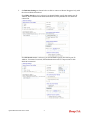
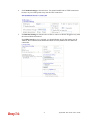
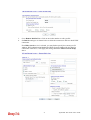
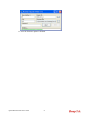
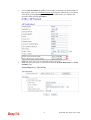
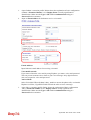
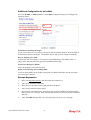
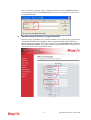
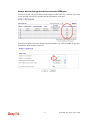
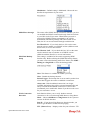
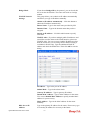
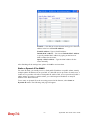
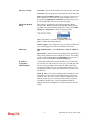
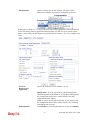
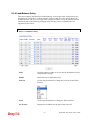
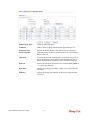
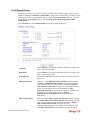
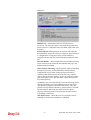
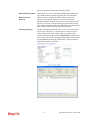
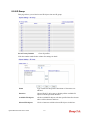
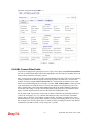
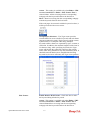
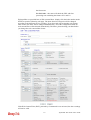
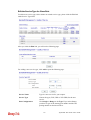
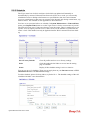
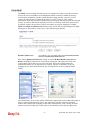
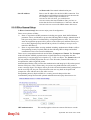
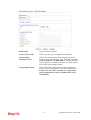
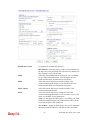
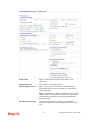
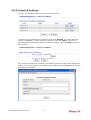
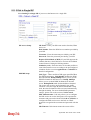
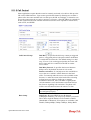
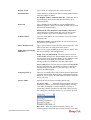
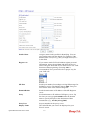
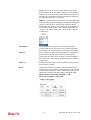
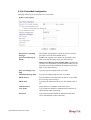
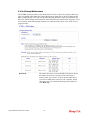
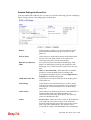
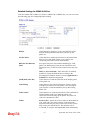
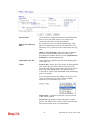
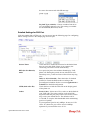
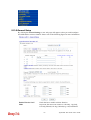
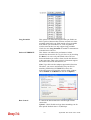
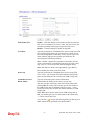
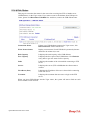
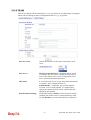
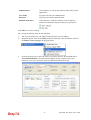
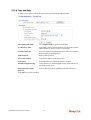
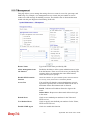
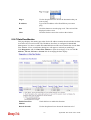
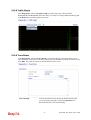
Specify mode, proposal and key life of each IKE phase,
Gateway etc.
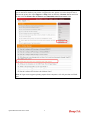
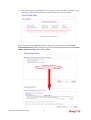
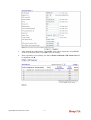
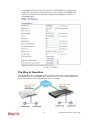
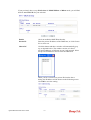
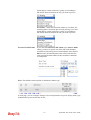
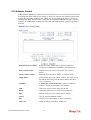
The window of advance setup is shown as below:
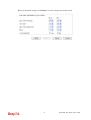
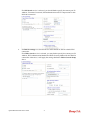
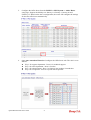
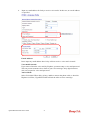
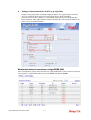
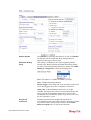
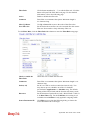
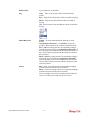
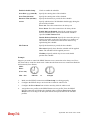
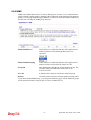
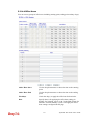
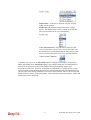
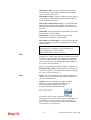
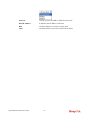
IKE phase 1 mode -Select from Main mode and
Aggressive mode. The ultimate outcome is to exchange
security proposals to create a protected secure channel.
Main mode is more secure than Aggressive mode since
more exchanges are done in a secure channel to set up the
IPSec session. However, the Aggressive mode is faster.
VigorIPPBX 2820 Series User’s Guide
251