1
Chapter 3 – Using the Web Management Software
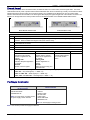
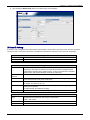
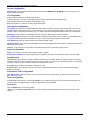
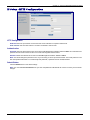
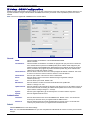
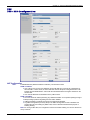
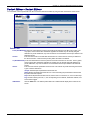
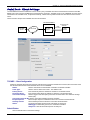
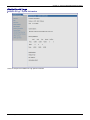
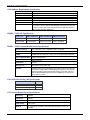
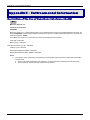
Add IKE Connection
47B
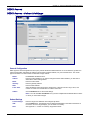
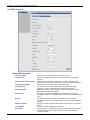
Add an IKE Connection
Connection Name
Compression
Perfect Forward Secrecy (PFS)
Authentication Method
Pre-Shared Key
Select Encryption
IKE Life Time
Key Life
Number of Retries
Local WAN IP
Local LAN
44
Enter a text name that will identify the connection for you.
Check the compression checkbox to enable IPCOMP, the compression
algorithm.
Check the PFS checkbox to enable PFS, a concept in which the newly
generated keys are unrelated to the older keys). This is enabled by default.
Authentication can be done using Pre-Shared Secrets.
The Pre-Shared Key must be agreed upon and shared by the VPN
endpoints; it must be configured at both endpoints of the tunnel.
Select the encryption method. 3DES is recommended. Options include:
3DES, AES-128, AES-192, AES-256
The duration for which the ISAKMP SA should last is from successful
negotiation to expiration. The default value is one hour and the maximum is 8
hours.
The duration for which the IPSec SA should last is from successful
negotiation to expiration. The default value is one hour and the maximum is
24 hours.
Specify the number of retries for the IPSec tunnel. Enter zero for unlimited
retries.
This is the interface initiating the IPSec tunnel.
Internal subnet of the local security gateway for which the security services
should be provided. If the RouteFinder acts as a host, this should be
configured as None.
Multi-Tech Systems, Inc. MultiModem rCell User Guide