1
Amazon Virtual Private Cloud User Guide
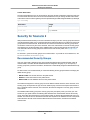
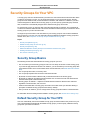
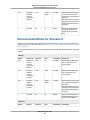
Recommended Rules for Scenario 1
For more information about network ACLs and how to use them, see Network ACLs (p. 70).
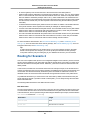
Important
We use the ephemeral port range 49152-65535. You can select a different range. For more
information, see Ephemeral Ports (p. 74).
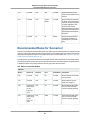
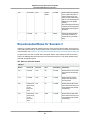
Recommended Rules for Scenario 1
Scenario 1 is a single subnet with instances that can receive and send Internet traffic. For more information,
see Scenario 1: VPC with a Single Public Subnet (p. 17).
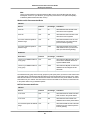
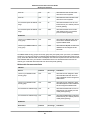
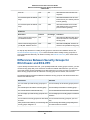
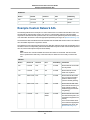
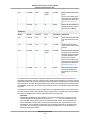
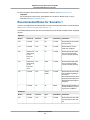
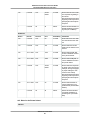
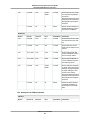
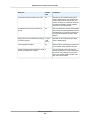
The following table shows the rules we recommended. They block all traffic except that which is explicitly
required.
Inbound
Rule #
Source IP
Protocol
Port
Allow/Deny
Comments
100
0.0.0.0/0
TCP
80
ALLOW
Allows inbound HTTP traffic
from anywhere
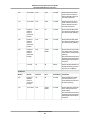
110
0.0.0.0/0
TCP
443
ALLOW
Allows inbound HTTPS
traffic from anywhere
120
Public IP ad- TCP
dress range
of your
home network
22
ALLOW
Allows inbound SSH traffic
from your home network
(over the Internet gateway)
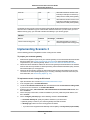
130
Public IP ad- TCP
dress range
of your
home network
3389
ALLOW
Allows inbound RDP traffic
from your home network
(over the Internet gateway)
140
0.0.0.0/0
TCP
4915265535
ALLOW
Allows inbound return traffic
from requests originating in
the subnet
See the important note at the
beginning of this topic about
specifying the correct ephemeral ports.
*
0.0.0.0/0
all
all
DENY
Denies all inbound traffic not
already handled by a preceding rule (not modifiable)
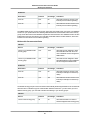
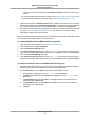
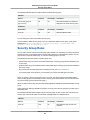
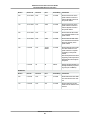
Rule #
Dest IP
Protocol
Port
Allow/Deny
Comments
100
0.0.0.0/0
TCP
80
ALLOW
Allows outbound HTTP traffic
from the subnet to the Internet
Outbound
API Version 2015-04-15
79