1
Amazon Virtual Private Cloud User Guide
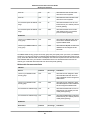
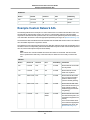
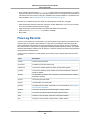
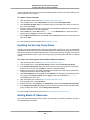
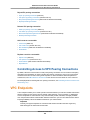
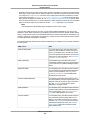
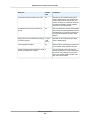
Recommended Rules for Scenario 2
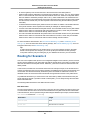
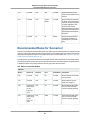
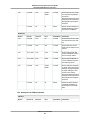
110
0.0.0.0/0
TCP
443
ALLOW
Allows outbound HTTPS
traffic from the subnet to the
Internet
120
0.0.0.0/0
TCP
4915265535
ALLOW
Allows outbound responses
to clients on the Internet (for
example, serving web pages
to people visiting the web
servers in the subnet)
See the important note at the
beginning of this topic about
specifying the correct ephemeral ports.
*
0.0.0.0/0
all
all
DENY
Denies all outbound traffic
not already handled by a
preceding rule (not modifiable)
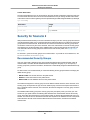
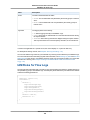
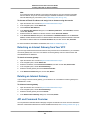
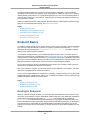
Recommended Rules for Scenario 2
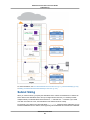
Scenario 2 is a public subnet with instances that can receive and send Internet traffic, and a private subnet
that can't receive traffic directly from the Internet. However, it can initiate traffic to the Internet (and receive
responses) through a NAT instance in the public subnet. For more information, see Scenario 2: VPC with
Public and Private Subnets (NAT) (p. 22).
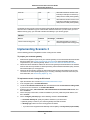
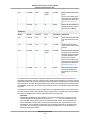
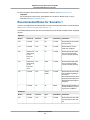
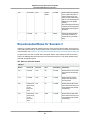
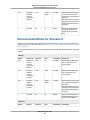
For this scenario you have a network ACL for the public subnet, and a separate one for the private subnet.
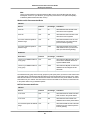
The following table shows the rules we recommend for each ACL. They block all traffic except that which
is explicitly required. They mostly mimic the security group rules for the scenario.
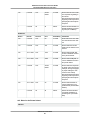
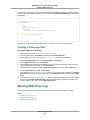
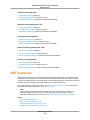
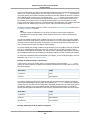
ACL Rules for the Public Subnet
Inbound
Rule #
Source IP
Protocol
Port
Allow/Deny
Comments
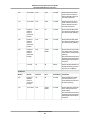
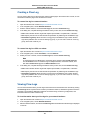
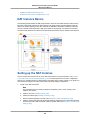
100
0.0.0.0/0
TCP
80
ALLOW
Allows inbound HTTP traffic
from anywhere
110
0.0.0.0/0
TCP
443
ALLOW
Allows inbound HTTPS
traffic from anywhere
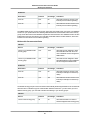
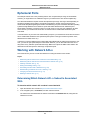
120
Public IP ad- TCP
dress range
of your
home network
22
ALLOW
Allows inbound SSH traffic
from your home network
(over the Internet gateway)
130
Public IP ad- TCP
dress range
of your
home network
3389
ALLOW
Allows inbound RDP traffic
from your home network
(over the Internet gateway)
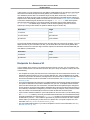
API Version 2015-04-15
80