1
36
Survey
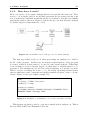
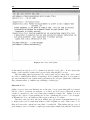
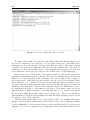
Figure 3.4. Scan with Splint
in the function test at row 15, column 2 in the file single_file.c. It also states the
name of the variable causing the bug and why this might be a bug.
The last thing that is presented for each found bug is a flag that can be used
in order to inhibit these kinds of warnings. If for example the user do not want to
get any warnings about format string parameters he can give Splint the additional
flag –formatconst to inhibit any warnings of that type.
Siproxd 0.7.0
Splint does not have any limitations on the size of a program that will be scanned
but in order to perform an analysis on a whole project some additional work is
required compared to the case when just scanning a single file. Splint does not
support the option of just passing the folder containing the source code as input,
as Flawfinder does, and thus another approach has to be taken.
The first, and probably the most simple way (in terms of implementation), is
to make some sort of script that makes a call for Splint for each of the source code
files and saves the output in some kind of result file. This makes the process of
performing a scan of a rather complex program quite simple but with the drawback