1
40
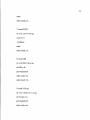
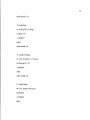
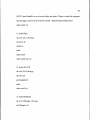
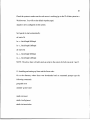
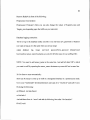
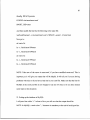
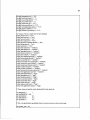
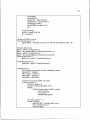
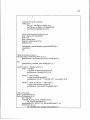
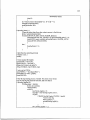
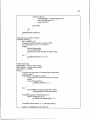
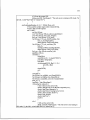
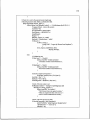
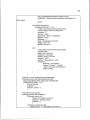
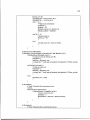
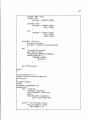
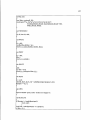
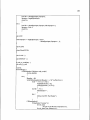
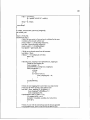
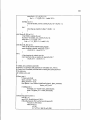
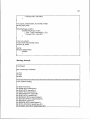
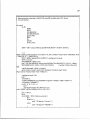
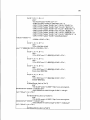
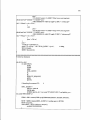
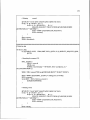
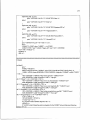
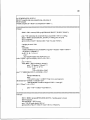
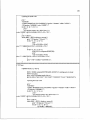
All these installation parameters of Snort can be changed in a Makefile including the
port, IP address and installation path. Key generation part is added for authentication
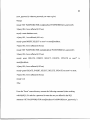
using certificates on the system. It can be removed from the Makefile if you do not want
to generate a key for the system on which Snort is installed. But, then make sure to
remove the SSL module from other *.pI.
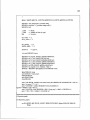
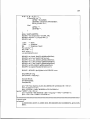
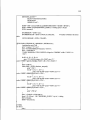
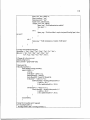
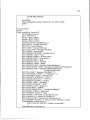
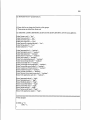
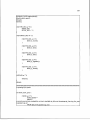
NOTE: Complete code can be found under Appendix B; it presents complete structured
details.
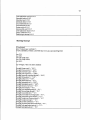
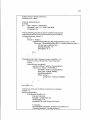
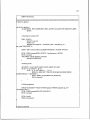
# License: This software is under GPL license, Date: 06 2005
ROOT = /opt/snort
CONFIGPATH = /etc/snort
BfN=snort.sh
BINPATH=/usr/sbin
certname
=
snort
life = 730
keylength= 1024
listen_port = 666
listenip= 127.0.0.1
#KEYREPOSITORY = $(CONFIGPATH)/ssl key
SSLPROGRAM = /usr/bin/openssl
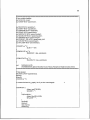
install : dir snort selfsign perlgd conf run by
dir:
mkdir -p $(ROOT)
mkdir -p $(CONFIGPATH)
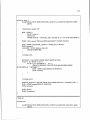
snort: @echo "snort install"
chmod 755 $(ROOT)
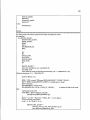
#keygen:
@if test -f $(KEY REPOSITORY)/$(certname).key; then \
echo 'key $(KEYREPOSITORY)/$(certname).key already exist'; \
else \ echo 'Generating RSA key $(KEYREPOSITORY)/$(certname).key'; \
$(SSLPROGRAM) genrsa -out $(KEY-REPOSITORY)/$(certname).key
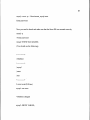
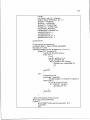
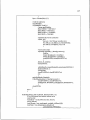
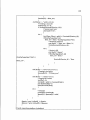
Figure 3.5 Makefile