1
UNCLASSIFIED
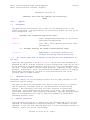
Severity: CAT III
Rule Version (STIG-ID): SRG-NET-000052-IDPS-000046
Rule Title: The IDPS must notify the user of organizationally defined security related changes to the user's account occurring during the
organizationally defined time period.
Vulnerability Discussion: Providing users with information regarding organizationally defined security related changes to the user's account
occurring during the organizationally defined time period, allows the user to determine if any unauthorized activity has occurred and gives them an
opportunity to notify administrators. Changes to the user account during a specific time period could be an indication of the account being
compromised. Hence, without notification to the user, the compromise could go undetected.
Check Content: Verify the system is configured to notify the user of organizationally defined security related changes to the user's account occurring during the
organizationally defined time period by logging on to the management console.
If the system does not notify the user of organizationally defined security related changes to the user's account occurring during the
organizationally defined time period, this is a finding.
Fix Text: Configure the IDPS management console to display the organizationally defined security-related changes to the user's account occurring
during the organizationally defined time period. CCI: CCI-001395
_____________________________________________________________
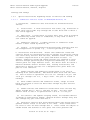
Group ID (Vulid): SRG-NET-000053-IDPS-000047
Group Title: SRG-NET-000053-IDPS-000047
Rule ID: SRG-NET-000053-IDPS-000047_rule
Severity: CAT III
Rule Version (STIG-ID): SRG-NET-000053-IDPS-000047
Rule Title: The IDPS must limit the number of concurrent sessions for each account to an organizationally defined number.
Vulnerability Discussion: This requirement addresses concurrent sessions for a given information system account and does not address
concurrent sessions by a single user via multiple accounts. In many products, this value defaults to unlimited which leaves the device open to DoS
attacks. An organizationally defined value should be configured.
Limiting the number of concurrent sessions to the device per any given account mitigates the risk associated with a Denial of Service (DoS) attack.
Check Content: View the user account management screens.
Verify the number of concurrent sessions setting is not set to unlimited.
Verify the number of concurrent sessions is set to an organizationally defined value.
If the number of concurrent sessions for accounts is set to unlimited, this is a finding. If the number of concurrent sessions is not set to an
file:///D|/IA security/SRG/U_IDPS_SRG_V1R0.3_manual-xccdf.xml[7/18/2012 14:57:29]