1
Set Up a VM-Series Firewall on the Citrix SDX Server
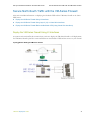
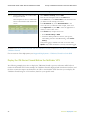
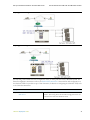
Secure North-South Traffic with the VM-Series Firewall
Set up the VM-Series Firewall to Process North-South Traffic Using L2 or Virtual Wire Interfaces (Continued)
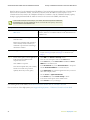
Step 2
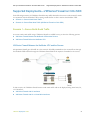
Re-cable the server-side interface
assigned to the NetScaler VPX.
Because the NetScaler VPX will reboot
when recabled, evaluate whether you
would like to perform this task during a
maintenance window.
Step 3
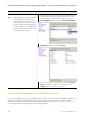
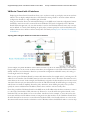
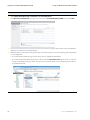
Configure the data interfaces.
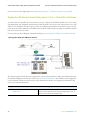
If you have already deployed a NetScaler VPX and are now adding
the VM-Series firewall on the SDX server, you have two ports
assigned to the VPX. When you deploy the VM-Series firewall, the
NetScaler VPX will now only require one port for handling
client-side traffic.
Therefore, before you configure the data interfaces the VM-Series,
you must remove the cable from the interface that connects the VPX
to the server farm and attach it to the firewall so that all traffic to the
server farm is processed by the firewall.
1.
This example shows the configuration for 2.
virtual wire interfaces.
3.
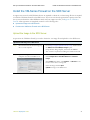
Launch the web interface of the firewall.
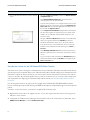
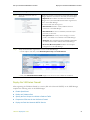
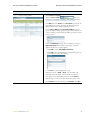
Select Network > Interfaces> Ethernet.
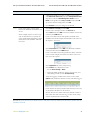
Click the link for an interface (for example ethernet 1/1) and
select the Interface Type as Layer2 or Virtual Wire.
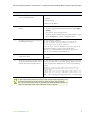
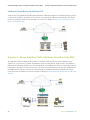
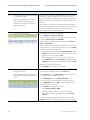
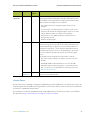
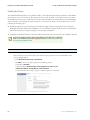
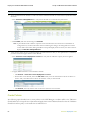
Virtual Wire Configuration
Each virtual wire interface (ethernet 1/1 and ethernet 1/2) must be
connected to a security zone and a virtual wire. To configure these
settings, select the Config tab and complete the following tasks:
a. In the Virtual wire drop-down click New Virtual Wire, define
a Name and assign the two data interfaces (ethernet 1/1 and
ethernet 1/2) to it, and then click OK.
When configuring ethernet 1/2, select this virtual wire.
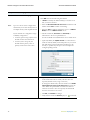
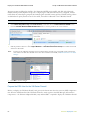
b. Select New Zone from the Security Zone drop-down, define
a Name for new zone, for example client, and then click OK.
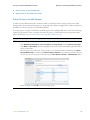
Layer 2 Configuration
For each Layer 2 interface, you require a security zone. Select the
Config tab and complete the following tasks:
a. Select New Zone from the Security Zone drop-down, define
a Name for new zone, for example client, and then click OK.
VM-Series Deployment Guide
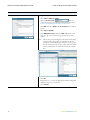
4.
Repeat steps 2 and 3 above for the other interface.
5.
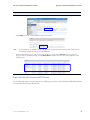
Click Commit to save changes to the firewall.
37