1
User Manual
Chapter 8
App Policy
Chapter 8
App Policy
This chapter introduces how to conFigure the App Policy functions
8.1 Introduction to App Policy
Employees often use Outlook to receive emails, Internet Explorer to browse websites, Instant Messengers (IM) such as
MSN/Skype to chat with friends, and P2P software such as BT / eDonkey / Xunlei / KaZaA / Kuro / ezPeer to download
illegal data. Among them, Email and IM are the channel for information leakage or virus intrusion, while P2Ps are the
bandwidth killers and may contain many spyware. What is worse, IM wastes employee's productivity by friends' interrupt
during the office hours. However, IM can save communication cost and even make communications more efficient so
that many enterprises are willing to allow IM.
Enterprises that emphasize network security may have deployed Email/Web auditing / management systems. In
comparison, IM and P2P lack the auditing/recording/behavior management/content management/bandwidth
management because IM/P2P software are optimized to tunnel through Firewalls. MSN / Yahoo / ICQ / AOL / Skype /
Google Talk can tunnel themselves to behave like Web/ Email to cheat Firewalls, tunnel through proxy servers, or even
encrypt themselves. Network administrators cannot manage them completely.
8.2 Scenario
1.
2.
3.
4.
CEO and CTO of the company should have full permission to access the Internet resources
Except for MSN, no other instant messenger software packages are allowed to use during office hours.
Besides Skype, there must be no other P2P applications during the office hours.
During the office hours, R&D members are not allowed to transfer files through Skype.
8.3 Methodology
1.
2.
3.
4.
Allow all traffic from CEO and CTO
Aside from CEO and CTO, employees can only use MSN. Other IMs are all blocked.
Aside from CEO and CTO, employees are allowed to use Skype, other P2P or VoIP software are strictly forbidden.
During the working hours, R&D members are not allowed to transfer files through Skype.
8.4 Steps
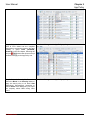
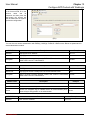
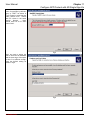
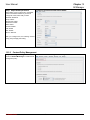
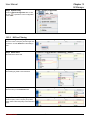
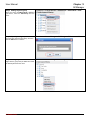
1. Enable the App Policy. Setup the scheduling of the working hours, and permit all traffic from the Boss group. Allow
MSN but block all other IM software.
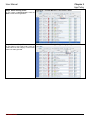
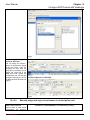
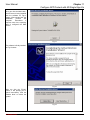
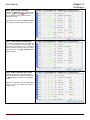
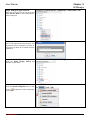
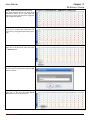
2. Allow Skype but deny all other P2P / VoIP software.
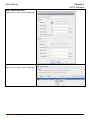
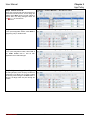
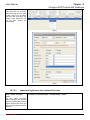
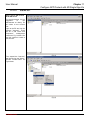
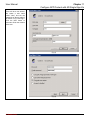
3. During the office hours, block R&D’s Skype File Transfer activities.
1.
2.
Note:
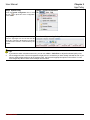
The default action of the device is Allow. So if you don’t set it to block but leave it as allow, it is better to set it to
never because that would greatly improve the throughput.
If the product is deployed outside the NAT / firewall, all the discovered traffic will be from the same IP address.
L7 Networks Inc.
47