1
NIDES Beta Release User Manual
90
5.5.4.6 Trojan Horse Rules
Two Trojan horse rules check for someone creating files or programs that will be executed
involuntarily by another user.
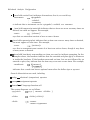
TrojanHorse This rule checks for the user executing system programs from other than
the list of directories specified by the rb_config file section PROGLOCATION (see
page 74). For example, if the user executes a program named ‘1s’that resides in the
directory /home/users/user1 (and this directory is not listed in the PROGLOCATION
list), this rule produces a “possible Trojan horse” alert.
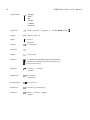
ChangeLoginFile This rule checks for a user modifying another user’s login configuration
files. The list of those files is configured in the rb_config file section LOGIN_CONFIG
(see page 72).
5.5.4.7
File and Device Access Rules
Eleven rules check for access to various files or devices that are either private or sensitive
with regard to system operation.
AccessPrivateFilel This rule checks for one user accessing a private file in another user’s
home directory. The list of private files is configured via the PRIVATE_FILE section
in the rb_config file (see page 74).
AccessPrivateFile2 This rule checks for a user accessing someone else’s mail spool file.
These files are found in /var/spool/mail.
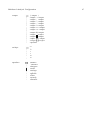
AccessSpecialFile This rule checks for unauthorized access to a configurable set of files
defined in the rb_config file section SPECIAL-FILE (see page 77). A file to be
protected is given a type id number; a user allowed to access that file is given the same
type id number in the USER-TYPE rb_config file section (see page 79). Multiple files
and multiple users can have the same type id number. This allows NIDES to report
access violations on a set of files by users not in a specified group. In addition, a single
user can have multiple type id entries. This allows NIDES to recognize that the user
has access to multiple types of files.
PasswordFileAccess This rule checks for access to the shadow password file. Only the
password authorization daemon should access this file. This rule generates an alert if
any other user touches that file.
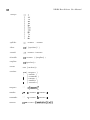
ModSystemExec This rule reports modification of system executables located in system
directories listed in the rb_config section PROGLOCATION (see page 74).
ReadSystemExec Users ordinarily should not read system executables. This rule reports
users doing so. Since scripts must be read in order to be executed, the rule ignores
reads of any files listed in the rb_config file section SYSTEM-SCRIPTS (see page 78).