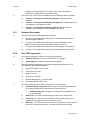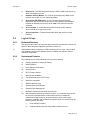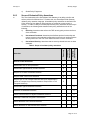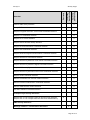
1
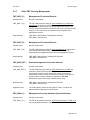
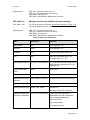
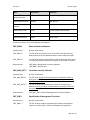
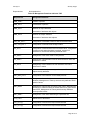
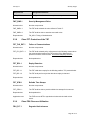
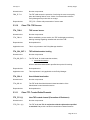
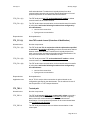
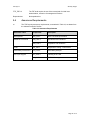
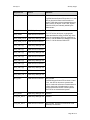
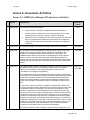
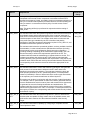
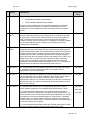
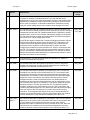
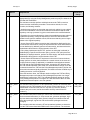
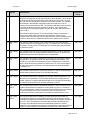
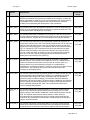
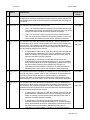
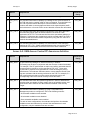
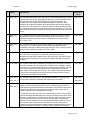
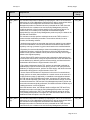
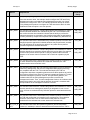
CA Layer 7 # Source Security Target Requirement Assurance Family the operational guidance, as well as one other value. For each period configured, the evaluator establishes a remote interactive session with the TOE. The evaluator then observes that the session is terminated after the configured time period. 34. FTA_SSL.4 35. FTP_ITC.1( 1) The evaluator shall perform the following tests: ATE_IND Test 1: The evaluator initiates an interactive local session with the TOE. The evaluator then follows the operational guidance to exit or log off the session and observes that the session has been terminated. Test 2: The evaluator initiates an interactive remote session with the TOE. The evaluator then follows the operational guidance to exit or log off the session and observes that the session has been terminated. The evaluator shall check the operational guidance in order to determine the mechanism by which secure communications are enabled. The evaluator shall also check the TSS, operational guidance, and other provided evidence to determine the means by which secure communications are facilitated. Based on this, the following analysis will be required: If cryptography is internal to the TOE, the evaluator shall verify that the product has been validated by FIPS 140-2 (if evaluating in the United States or Canada) or an equivalent national standard for the nation in which the evaluation is being conducted. If cryptography is provided by the Operational Environment, the evaluator shall review the operational guidance, ST, and any available design documentation to see how cryptography is utilized and to verify that the functions used have been validated by FIPS 140-2 (if evaluating in the United States or Canada) or an equivalent national standard for the nation in which the evaluation is being conducted. AGD_OPE ASE_TSS 36. FTP_ITC.1( 1) The evaluator shall test this capability by enabling secure communications on the TOE and placing a packet sniffer on the local network. They shall then use the TOE to perform actions that require communications to all trusted IT products with which it communicates and observe the captured packet traffic that is directed to or from the TOE to ensure that their contents are obfuscated. ATE_IND 37. FTP_ITC.1( 2) The evaluator shall check the operational guidance in order to determine the mechanism by which secure communications are enabled. The evaluator shall also check the TSS, operational guidance, and other available evidence to determine the means by which secure communications are facilitated. Based on this, the following analysis will be required: AGD_OPE If cryptography is internal to the TOE, the evaluator shall verify that the product has been validated by FIPS 140-2 (if evaluating in the United States or Canada) or an equivalent national standard for the nation in which the evaluation is being conducted. If cryptography is provided by the Operational Environment, the evaluator shall review the operational guidance, ST, and any available design documentation to see how cryptography is utilized and to verify that the functions used have been validated by FIPS 140-2 (if evaluating in the United States or Canada) or an equivalent national ASE_TSS Page 69 of 74