1
Alternate Data Streams in Windows NT/2000/XP.
Alternate Data Streams (ADS) have been available to Windows NT and 2000 systems ever since the first
version of NTFS. ADS was originally created to allow Windows NT to support Macintosh computers
which keeps some file information in Resource Forks.
While ADS was created for Mac file support, any user can utilize ADS to hide data or files within a
system which uses NTFS formatted drives. It is easy to hide data with ADS and only requires a few steps
as shown by the following:
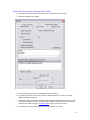
1. From command line in Windows NT/2000 Pro enter C: to move to drive root
2. Enter “notepad boot.ini:ADSFile.txt”
3. Notepad asks to create the file, choose OK
4. Type in some text to hide
5. Choose file | save
6. Exit notepad
7. Enter “notepad boot.ini:ADSFile.txt”
8. Confirm the text you entered is still there
Now try the same thing without appending the ADS to any file.
1. From command line in Windows NT/2000 Pro enter C: to move to drive root
2. Enter “notepad :AnotherADSFile.txt”
3. Notepad ask to create the file choose OK
4. Type in some text to hide
5. Choose file | save
6. Exit notepad
7. Enter “notepad :AnotherADSFile.txt”
8. Confirm the text you entered is still there
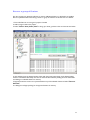
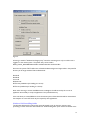
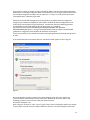
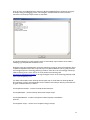
While ADS files are not viewable in Windows NT/2000 through normal file views, there are several
utilities which allow you to detect the presence of ADS files. Unfortunately these utilities do not always
detect the presence of all ADS files. In particular ADS files which have not been created as appended to
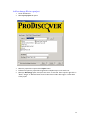
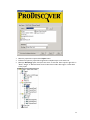
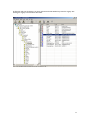
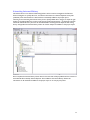
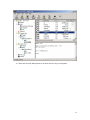
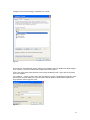
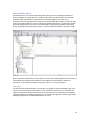
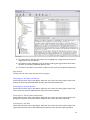
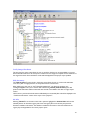
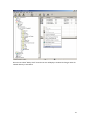
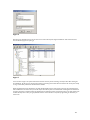
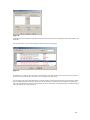
a visible file are sometimes not reported. ProDiscover detects and displays all ADS files and displays
them in "Content View" highlighted in Red by default.
System $ meta files in Windows NT/2000/XP.
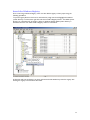
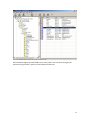
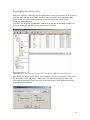
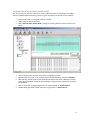
When viewing an NTFS partition in Content-view users will notice files not normally seen which all begin
with $ and are highlighted in green by default. These files are NTFS meta files and contain a great deal of
information about the file system.
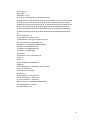
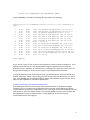
Each metafile has an inode number and description as listed here:
Inode 0 $MFT Master File Table - An index of every file
Inode 1 $MFTMirr A backup copy of the first 4 records of the MFT
Inode 2 $LogFile Transactional logging file
Inode 3 $Volume Serial number, creation time, dirty flag
Inode 4 $AttrDef Attribute definitions
Inode 5 . (dot) Root directory of the disk
Inode 6 $Bitmap Contains volume's cluster map (in-use vs. free)
Inode 7 $Boot Boot record of the volume
Inode 8 $BadClus Lists bad clusters on the volume
94