1
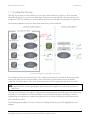
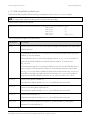
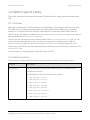
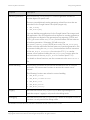
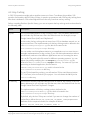
Secure Key Box User Guide 1 Introduction 1.1.2 Nomenclature This User Guide uses the terms “secure”, “protect”, ”white-box protected”, “safe”, “tamper resistance” and variations of each to convey very specific concepts — indeed, concepts that are far more specific and limited in their meanings than many meanings often associated with such terms in everyday usage. At the risk of stating the obvious, as used herein, none of these terms describe an absolute condition. Use of SKB in compliance with this User Guide will not render any application or data absolutely secure, absolutely protected or absolutely safe from unauthorized accessing, use or manipulation. Nor will it render any application or data absolutely tamper resistant. In addition, use of these terms is not intended to convey a promise or warranty that SKB will never contain a bug or error, or that SKB will always operate without error. As used in this User Guide: “secure” and variations of “secure” refer to data objects, the values of which reside in a cryptographic container and are white-box protected, and that can be operated on by SKB functions despite the fact that they are not revealed in plain form. “protected”, “white-box protected” and variations of these terms mean that a value has been subjected to some cryptographic processing that has resulted in it being placed in a container that seeks to render the value inaccessible in plain form to the outside world. “safe”, “safely”, “safer” and variations of these terms refer to actions or objects that when processed in accordance with this User Guide will not compromise the security protections provided by SKB. “tamper resistance” and variations of this term refer to the application of whiteCryption’s Code Protection product to render it more difficult for unauthorized parties to engage in reverse engineering and code modification. 1.1.3 Purpose of SKB Cryptographic algorithms and keys are used to protect sensitive data, authenticate communication partners, verify signatures, and implement various other security schemes. A common weak point of cryptographic algorithms in today’s open architectures, such as smartphones, tablets, and desktops, is that the cryptographic keys are revealed in the code or memory at some point. Hackers can monitor such devices with special tools and extract the secret cryptographic keys. Without an efficient protection of cryptographic keys, security features may be compromised. SKB is designed to prevent such attacks by encrypting and hiding cryptographic keys in the code and memory. 1.1.4 White-Box Cryptography The term “white-box cryptography” is used to describe a secure implementation of cryptographic algorithms in an execution environment that is fully observable and modifiable by an attacker, such as a desktop computer or a mobile device. It is different from black-box cryptography where the Copyright © 2000-2015, whiteCryption Corporation. All rights reserved. Copyright © 2004-2015, Intertrust Technologies Corporation. All rights reserved. Page 10 of 137