1
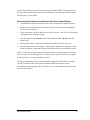
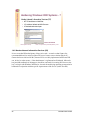
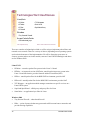
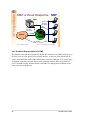
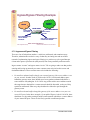
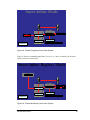
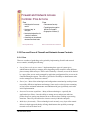
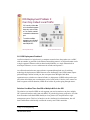
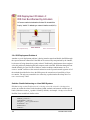
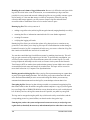
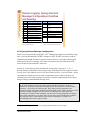
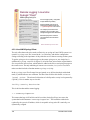
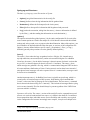
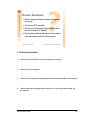
DMZ: A Visual Perspective
Protected
Network
DMZ
Allow: TCP 80, 443, 22, etc.
Allow: UDP 53
Deny: All others!
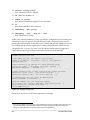
interface2
Allow: TCP 80, 443, etc.
Allow: UDP 53
Deny: All others!
interface1
interface3
Internet
Internet
Deny: All inbound!
© 2003 Carnegie Mellon University
Module 2: Firewalls and Network Access Controls–Slide 13
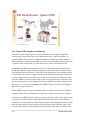
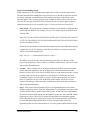
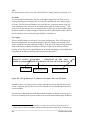
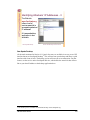
2.6.2 Graphical Representation of a DMZ
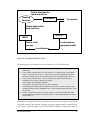
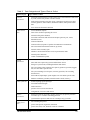
The diagram in the slide above graphically depicts the construction of a DMZ which is set up
to allow access to a few specific services to the Internet—in this case, Web (80 and 443 for
secure and standard http traffic) and DNS for name resolution (UDP port 53). It is set to deny
all inbound connections from the Internet to the protected network, and to only allow TCP
port 22 for SSH from the internal network to the DMZ (for management) in addition to the
other ports open to the Internet.
88
CMU/SEI-2004-HB-001