1
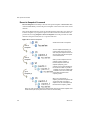
17 Managing Users, Groups, Permissions, and Roles 17 This chapter describes users, groups, permissions, and roles. VirtualCenter and ESX Server hosts determine the level of access for the user based on the permissions assigned to the user. The combination of user name, password, and permissions is the mechanism by which VirtualCenter and ESX Server hosts authenticate a user for access and authorize the user to perform activities. The servers and hosts maintain lists of authorized users and the permissions assigned to each user. NOTE You must be in Admin view for the Admin > Roles menu item to be enabled. Privileges define basic individual rights required to perform actions and read properties. ESX Server and VirtualCenter use sets of privileges, or roles, to control which individual users or groups can access particular VMware Infrastructure objects. ESX Server and VirtualCenter provide a set of pre‐established roles. You can also create new roles. The privileges and roles assigned on an ESX Server host are separate from the privileges and roles assigned on a VirtualCenter Server. If you have privileges and roles assigned on an ESX Server host and then add that host to the VirtualCenter Server inventory, only the privileges and roles assigned through the VirtualCenter Server are recognized. If you then remove the host from the VirtualCenter Server inventory, the previously set ESX Server host privileges and roles are used. For a complete list of privileges available, see Appendix A, “Defined Privileges,” on page 327. This chapter contains the following topics: “Access Elements” on page 262 “Access Rules” on page 262 VMware, Inc. 261