1
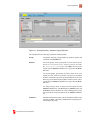
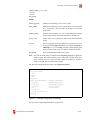
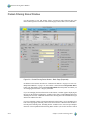
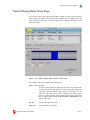
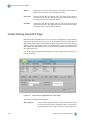
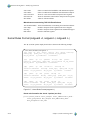
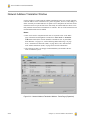
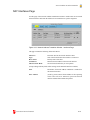
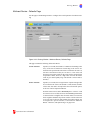
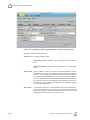
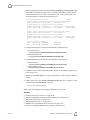
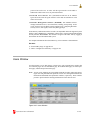
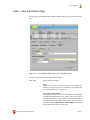
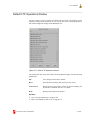
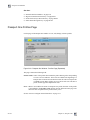
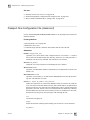
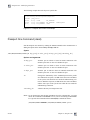
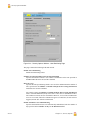
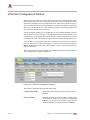
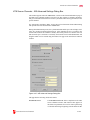
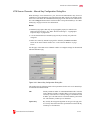
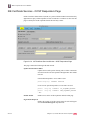
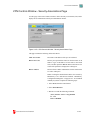
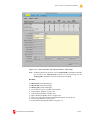
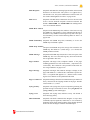
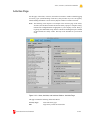
Split Domain Name System Window
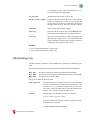
Any
Allows zone transfers with any host and network.
None
Does not allow zone transfers.
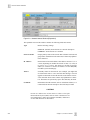
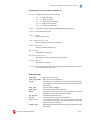
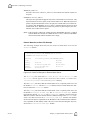
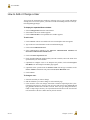
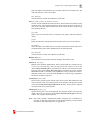
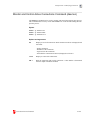
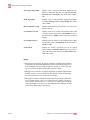
Private Name Server
Internal Interfaces
Lists the IP addresses of the internal interfaces of the firewall. Check each interface on which the internal DNS
server will listen.
Forwarder Addresses
IP addresses (separated with a space, new line, or carriage
return) for the name server to contact if it receives a
request for a name outside its authority. This read-only
field shows the external interface address(es) from the
Network Interfaces window.
Privileged Addresses
IP addresses (separated with a space, new line, or carriage
return) of hosts and networks that are permitted to make
zone transfers.
Any
Allows zone transfers with any host and network.
None
Does not allow zone transfers.
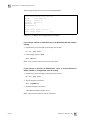
Note: You cannot use subnetted IP addresses on the internal side of the firewall if you
want to resolve names on the firewall. The /etc/resolv.conf file does not allow a
classless IP address as the address of the name server.
See also “DNS Resolver Configuration File (resolv.conf)” on page II-138.
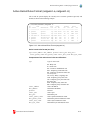
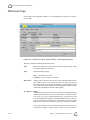
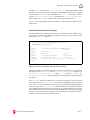
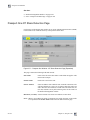
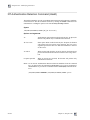
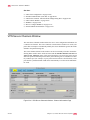
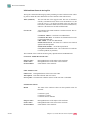
DNS Zones Page
7
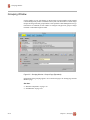
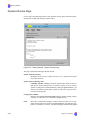
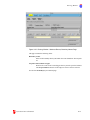
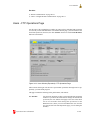
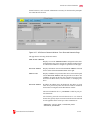
Use this page of the Split DNS window to provide the zone name, role, and information
sources for the internal and external name servers and to provide connectivity to the Internet for external name servers.
CAUTION!
Do not enter in-addr.arpa domains. The CyberGuard Firewall
automatically constructs these domains from the host data.
CyberGuard Firewall Manual
II-117