1
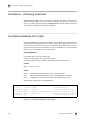
VPN - Underlying Constructs
stop
Signals vpnguard(1M) to terminate/exit.
ike-log
Starts and stops IKE exchange debug logging. The default log file is
/var/adm/log/ike.log.
events
Sets the lowest priority syslog priority level message to be sent by the
policy manager (vpnguard(1M)). The -l level specified along with all
higher (lower numbered) priorities are enabled and will be sent to
syslog. Note that the final syslog destination depends on the syslog configuration. See syslog.conf(4).
trace
If trace logging is enabled (-l level option is non-zero), all event (syslog)
messages are sent to the trace file. The default trace file is
/var/tmp/vpn.log.
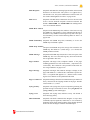
-l level
Sets the debug level. Stops logging if the level is 0.
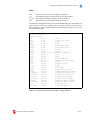
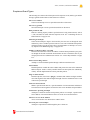
The following are the acceptable levels listed from highest to lowest priority.
EMERG
0
system is unusable
ALERT
1
action must be taken immediately
CRIT
2
critical conditions
ERR
3
error conditions
WARNING
4
warning conditions
NOTICE
5
normal but significant condition
INFO
6
informational messages
DEBUG
7
debug-level messages
-f logfile
Writes to the specified file.
-x max_size
Sets the maximum size in Kilobytes that the log file is allowed to grow
before logging is disabled. The default is 4096 KB (4 MB).
-c
Clears the log file.
-V
Produces a more formatted output to the IKE log. This format is easier to
read and output records span multiple lines.
-v
Verbose output. Displays vpnguard(1M) control connection status.
-q
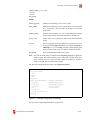
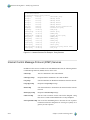
Queries the current settings. The -v option can be used to produce an easily readable table of the current settings; otherwise a one-line output is
produced in the following format:
log:file:level:flags:max:size:lines[:msg] where:
log - Log name (IKE, EVENTS, or TRACE)
II-318
Chapter 13, Virtual Private Network (VPN)